Compliance

Compliance proven, not declared.

Every requirement in your frameworks becomes a task, every task awaits its evidence, and every piece of evidence is timestamped. On audit day, everything is already there.

Compliance option available from the Premium plan. See plans

ISO 27001ISO 27002NIS 2RGPDMicrosoft 365SAIL

64 %

Evidence validated · ISO 27001

From requirement to evidence

Cybernetics links every requirement of the standard to the actual work and the documents that prove it.

  1. 01

    Requirement

    The framework clauses are imported and organized, ready to be tracked.

    ISO 27001 · 5.2 Policy

  2. 02

    Task

    Each requirement is broken down into tasks with an owner and a priority.

    Write the policy · High

  3. 03

    Evidence

    Uploaded documents or automated tests: the task is justified, not just ticked.

    PSSI v3.2 signee.pdf

  4. 04

    Audit

    The score updates and the PDF or CSV export is ready for your auditor.

    PDF export · ISO 27001

Evidence, at the heart of the product

An auditor doesn't take your word for it: Cybernetics gathers what convinces them.

  • PDF, DOCX…

    Uploaded documents

    Signed policies, procedures, meeting minutes: each piece of evidence is attached to its task and requirement.

  • 50 / 74

    Automated tests

    Encryption, antivirus, MFA, patches: your connectors and the agent provide evidence continuously.

  • 100%

    Timestamped history

    Who ticked what, who uploaded which evidence and when: the activity log is never erased.

  • 68%

    One piece of evidence, several frameworks

    Evidence shared by ISO 27001, NIS 2 or GDPR is provided only once: that's evidence overlap.

All your compliance, in one place

From frameworks to the auditor's export, shown in the real interface.

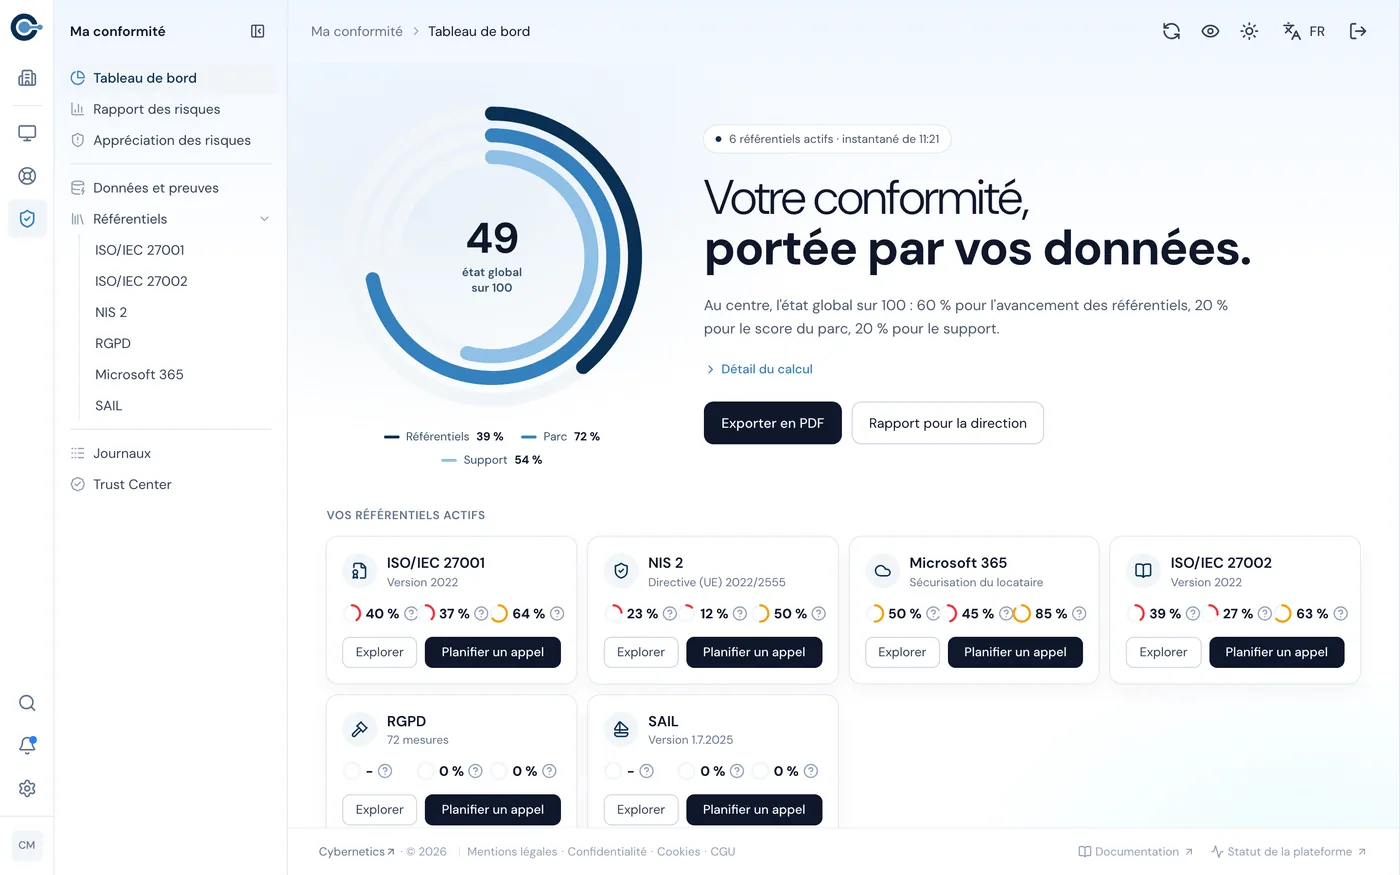
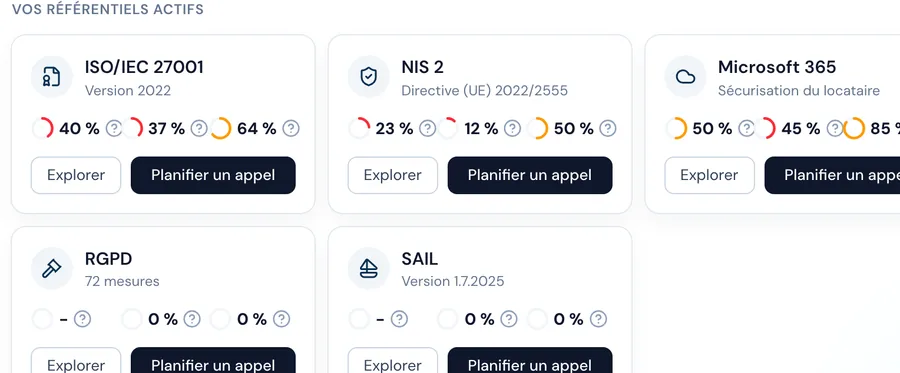
Compliance dashboard: overall status and active frameworksActive frameworks as cards: ISO/IEC 27001, NIS 2, Microsoft 365, ISO/IEC 27002, GDPR and SAIL

01 Frameworks

Six frameworks, one single dashboard

Turn on the frameworks that apply to you and track, for each one, evidence completion and the progress of controls and tasks.

  • ISO 27001, 27002, NIS 2GDPR, Microsoft 365, SAIL
  • One-click activationFrom the Discover page
  • Evidence, controls and tasksThree rings per framework
  • Custom controlsAdd your own requirements
Read the guide (in French)
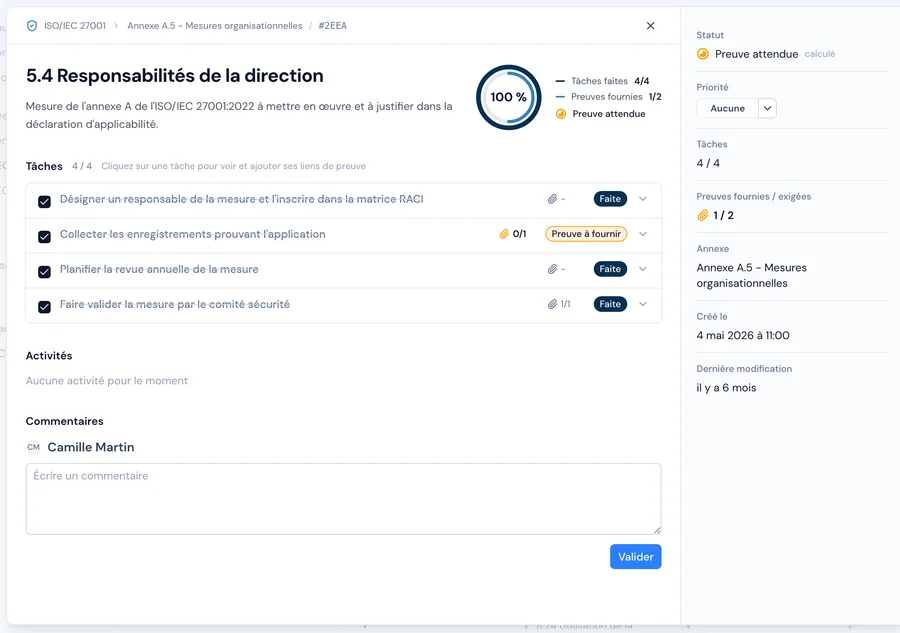
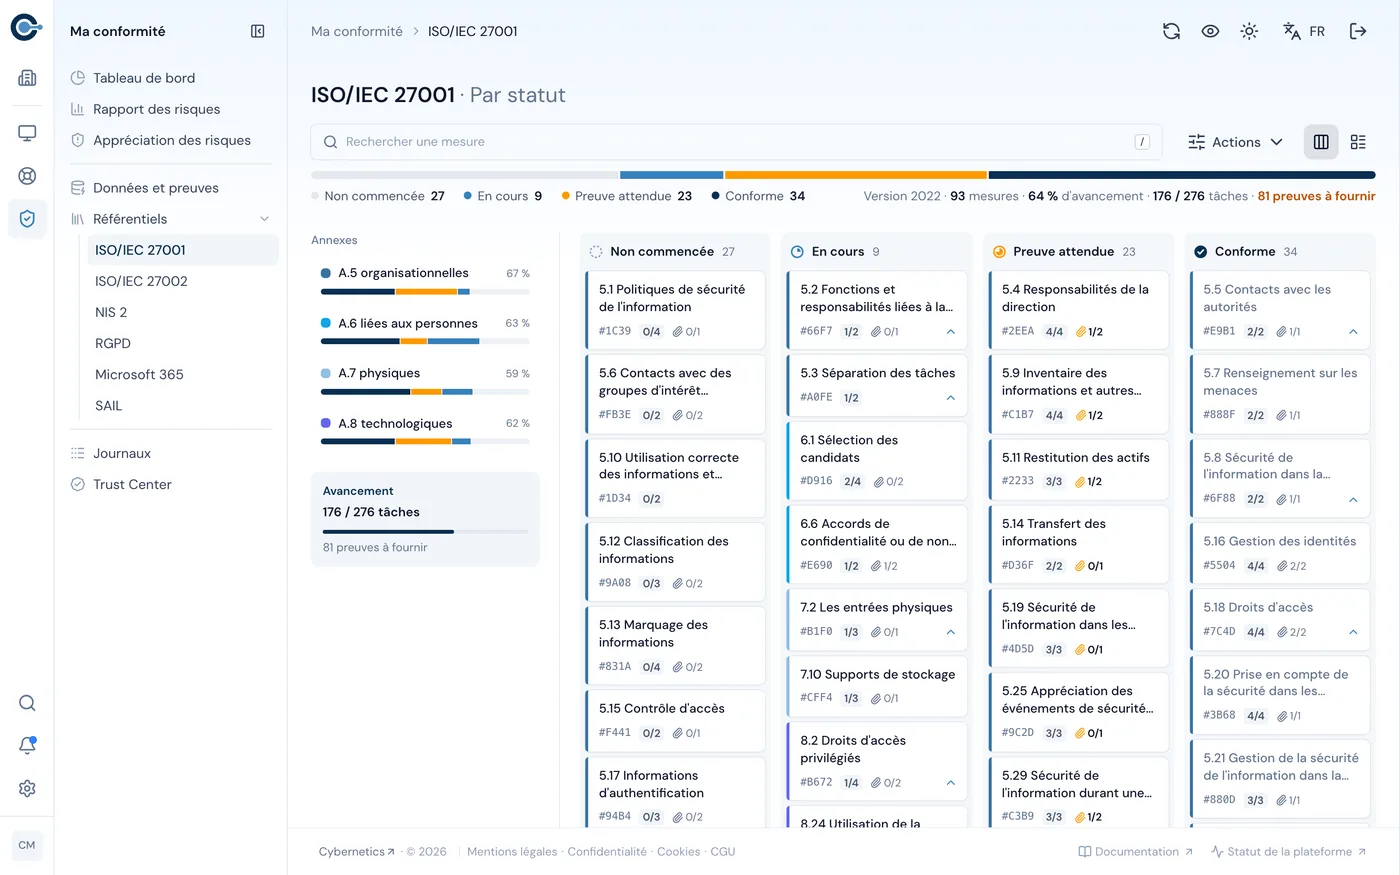
ISO/IEC 27001 kanban: measures by status and evidence progressISO/IEC 27001 measure 5.4: tasks, expected evidence, activity and comments

02 Controls and tasks

Every clause, broken into tasks

Go through the framework clause by clause. Each requirement carries its tasks, their priority, their owner and the expected evidence.

  • By clauseContext, leadership, operations…
  • Assigned ownerWho does what
  • PriorityHigh, medium, low
  • Filter by statusWhat still needs proof
Read the guide (in French)
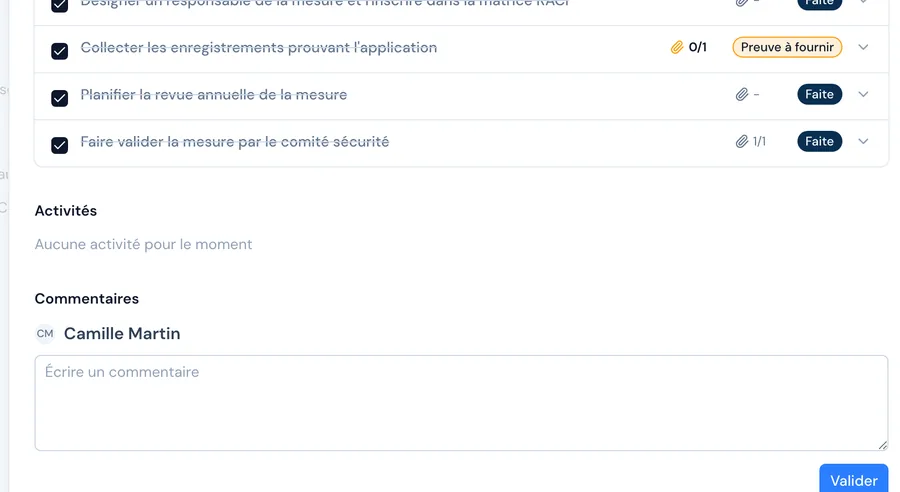
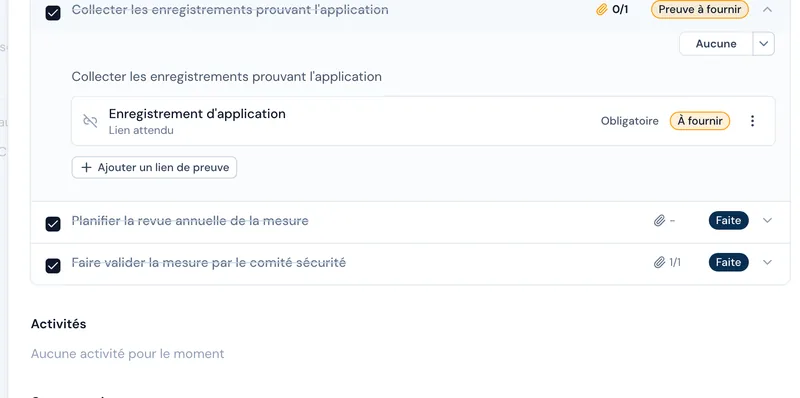
Tasks, activity and comments of a measureExpected evidence for a task: application record, to be provided

03 Evidence

Evidence attached and timestamped

Upload the evidence directly on the task. It switches to “Provided”, the score goes up and the activity is logged with its author.

  • Upload on the taskDocument or link
  • Evidence statusMissing, provided
  • Activity logAuthor, date, action
  • CommentsManagement approvals
Read the guide (in French)
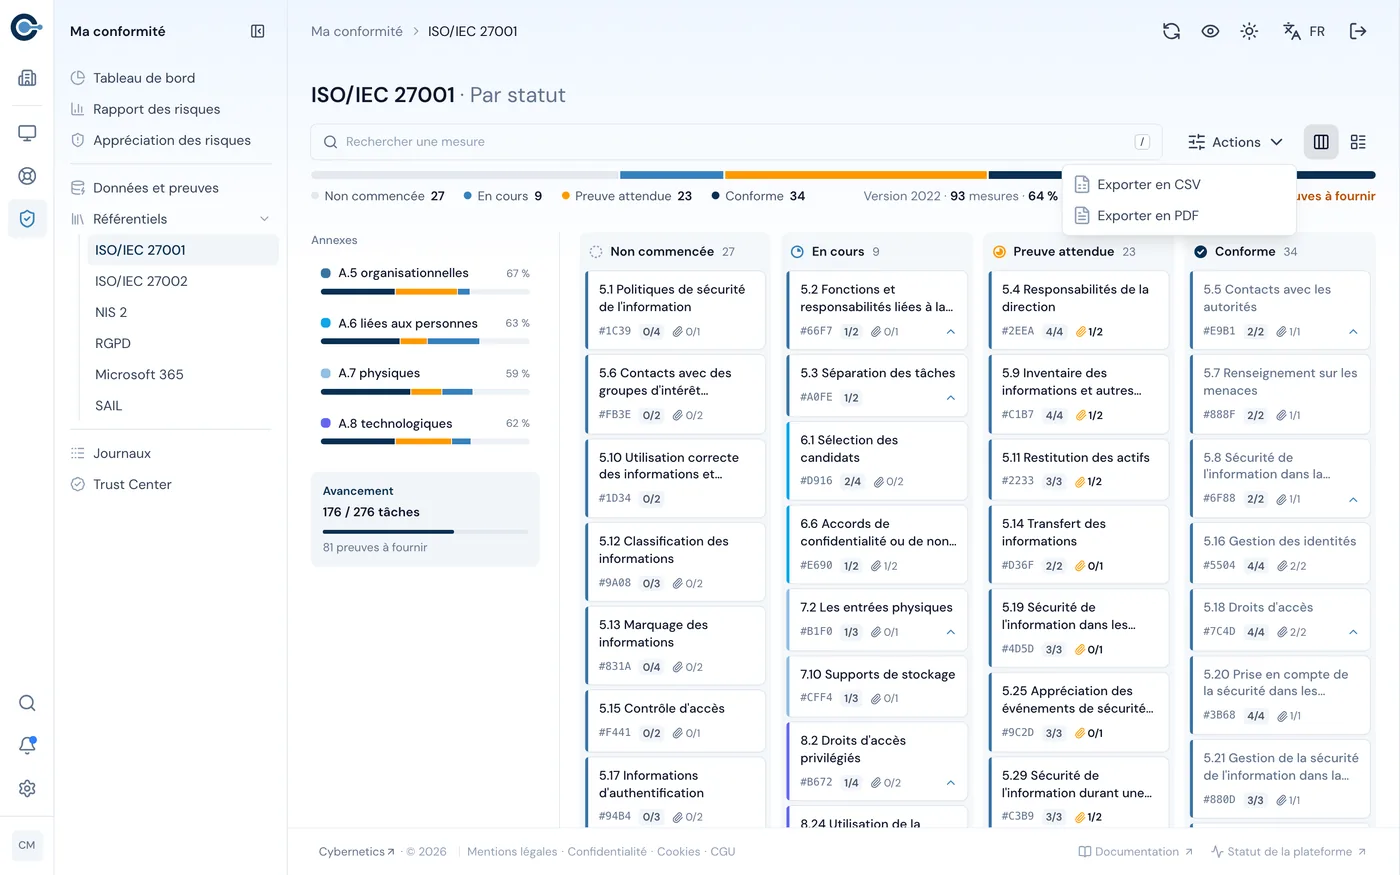
ISO/IEC 27001 kanban and Actions menu: CSV and PDF export

04 Audit

Audit-ready, at any time

An overview by priority and by clause, and a PDF or CSV export to hand to your auditor or your management.

  • View by clauseTasks done out of total
  • PDF exportFor management
  • CSV exportFor the auditor
  • ProgressVisible over time
Read the guide (in French)

Six frameworks tracked continuously

For each one, the share of validated evidence and completed controls.

  • ISO/IEC 27001

    Information security management system

    Evidence validated 64 %

    Controls completed 68 %

  • ISO/IEC 27002

    Information security controls

    Evidence validated 29 %

    Controls completed 48 %

  • Microsoft 365

    Microsoft 365 security best practices

    Evidence validated 56 %

    Controls completed 61 %

  • RGPD

    Personal data security

    Evidence validated 56 %

    Controls completed 60 %

  • NIS 2

    European directive on network security

    Evidence validated 33 %

    Controls completed 38 %

  • SAIL

    Security of AI systems

    Evidence validated 0 %

    Controls completed 25 %

Example from a demo organization.

Your compliance, proven continuously

Stop preparing your audits by hand. Cybernetics gathers your evidence as you go, so you are always ready.

Compliance option available from the Premium plan.